What You Tell a Chatbot Doesn't Stay Between You Two
Have you ever told a chatbot something you wouldn’t tell a coworker?
Maybe it was late. You had a weird test result, or a fight with your sister, or a letter from the IRS you didn’t understand. So you opened a chatbot and dumped the whole thing in: a big copy and paste, or the PDF dragged straight into the chat. Maybe there were names and numbers in there, maybe an account number. The chatbot is patient, and it answers right away.
Most of us have done this. I have.
It feels like a private conversation. It isn’t one, not the way a talk with your doctor is. Nobody’s reading your chats for fun, and the companies aren’t villains. But your words go to someone else’s computer, and a few things can happen to them there that you never pictured when you hit Enter. Here are the real ones, without the tech-speak.
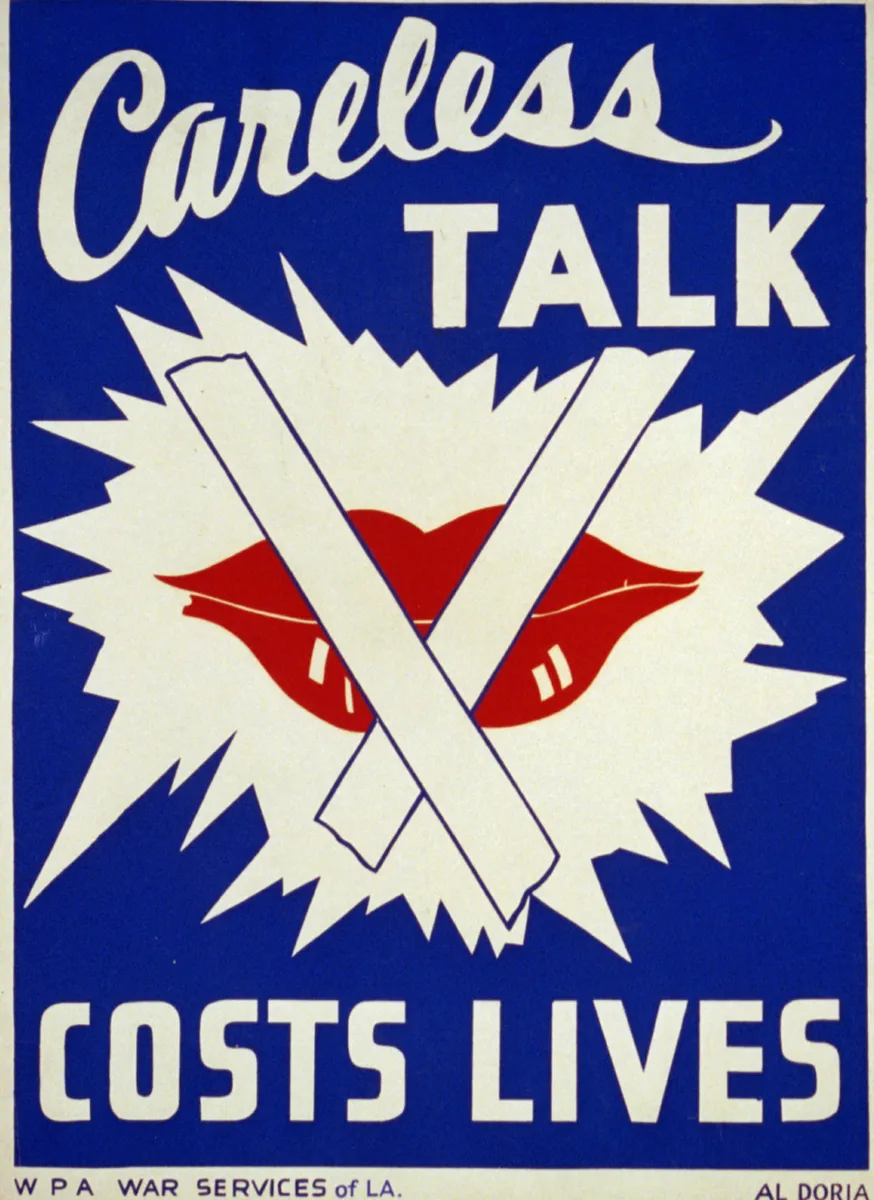
“Careless talk costs lives.” A World War II poster by Al Doria for the WPA War Services of Los Angeles, 1941–43. The advice aged well. (Library of Congress, Work Projects Administration Poster Collection.)
Risk 1: Your chats can become training material
When you use the free or personal version of the big chatbots, your conversations can be used to improve the next version of the AI. In 2025, Stanford researchers read the privacy policies of six major AI companies: Amazon, Anthropic, Google, Meta, Microsoft and OpenAI. All six appear to use people’s chats to train their models by default. You have to find the setting and switch it off. Stanford also found that some companies let human staff review chat transcripts as part of that training.
That doesn’t mean your chat gets published. It does mean it’s kept and handled by people and systems you’ll never see.
Where to find the off switch
It takes about a minute per app. Menus move around, so each step links to the company’s own help page. Switching it off covers your chats from now on. It doesn’t pull back anything already used for training.
- ChatGPT: Settings → Data controls → turn off “Improve the model for everyone.” On the phone app, tap your profile icon to get to Settings. (OpenAI help)
- Gemini: on gemini.google.com, click Settings & help → Activity, then near the top click On → Turn off (or “Turn off and delete activity”). Google says that with this off, your chats aren’t used to train its models, but they’re still kept for up to 72 hours. (Google help)
- Claude: click your name → Settings → Privacy → turn off “Help improve Claude.” (Anthropic help)
- Microsoft Copilot: your profile icon → Settings → Privacy, and turn off the model-training switches (one for typed chats, one for voice). (Microsoft help)
- Grok: on X, go to Settings and privacy → Privacy and safety → Grok & Third-Party Collaborators, and uncheck the data-sharing box. (Engadget, X help)
- Meta AI (in Facebook, Instagram and WhatsApp): there’s no off switch in the U.S. As Engadget put it in September 2026, “Meta doesn’t allow US users to opt out at all.” In the EU and UK, you can object with a form in Meta’s Privacy Center. (Engadget)
If you use a chatbot through work, your company’s plan may already keep your chats out of training. Ask your IT team before you assume.
Risk 2: Real people may read them, and “delete” has fine print
Google’s own Gemini privacy page says it plainly: “A subset of chats are reviewed by human reviewers,” and “Reviewed chats are retained for up to three years.” Then comes the line every chatbot user should read: “Please don’t enter confidential information that you wouldn’t want a reviewer to see.”
How long your words are kept depends on the company and your settings:
Sources: Google Gemini Apps Privacy Hub (updated Sept 2026) · Anthropic, Updates to our consumer terms (Aug 2025).
And deleting a chat isn’t always the end of it. In 2025, a court order in The New York Times’ copyright lawsuit against OpenAI forced the company to keep ChatGPT conversations, including ones users had deleted, for months. OpenAI says that obligation ended on September 26, 2025. Later, a judge ordered OpenAI to hand over about 20 million ChatGPT conversations to the newspaper’s side, run through what OpenAI calls a “de-identifying procedure” first.
Risk 3: There’s no doctor–patient privilege
OpenAI’s CEO, Sam Altman, said it himself in July 2025: “People talk about the most personal sh** in their lives to ChatGPT.” With a therapist, a lawyer or a doctor, he said, “there’s legal privilege for it… And we haven’t figured that out yet for when you talk to ChatGPT.”
In plain English: if a court or a lawsuit asks for your chats, nothing like the protection your therapist has applies to them. The New York Times case shows that isn’t just theoretical.
Risk 4: The “share” button can make it public
This one has already happened more than once.
People clicked “share” to send a chat to a friend, not realizing the link could land in search results. OpenAI called its version “a short-lived experiment” and pulled it. Meta’s AI app had a “Discover” feed where people published chats that TechCrunch found included home addresses and court details. Meta has since removed that feed.
Risk 5: Bugs happen
In March 2023, a ChatGPT bug let some users see the titles of other people’s chats, and may have exposed names, emails and the last four card digits of 1.2% of Plus subscribers active during a nine-hour window. Full card numbers weren’t exposed. Still: anything stored on a server can leak from it.
How many of us are doing this anyway?
Lots. In a 2025 survey of more than 6,500 people in seven countries by the National Cybersecurity Alliance and CybSafe, 43% of people who use AI at work said they’d shared sensitive workplace information with AI tools without their employer knowing. And it’s not just work. A KFF poll of 1,343 U.S. adults in early 2026 found that 13% had uploaded or shared personal medical information with an AI tool. Meanwhile 77% said they were concerned about the privacy of medical information they give AI.
We’re worried, and we do it anyway. The chatbot is useful, and the risk is invisible.
The fair counterpoint
None of this means you should never touch ChatGPT or Gemini. These companies have serious security teams. Business and enterprise plans generally don’t train on your data. Most consumer chatbots now let you turn off training or use a temporary chat. And most chats are ordinary: an OpenAI-backed study of about 1.1 million ChatGPT messages found only 1.9% were about relationships and personal reflection. Most were people asking questions or getting a task done.
The line isn’t “AI bad.” It’s this: would you be OK if a stranger at a tech company read it, or if it came up in a lawsuit? If yes, use whatever’s handy. If not, don’t paste it into someone else’s computer.
Why local AI is safer
Here’s the alternative most people don’t know exists. You can run an AI model on your own computer. Some AI companies, Meta, Mistral, Alibaba (Qwen) and DeepSeek among them, release “open” models: the AI itself is a file you can download, rather than a service you log into. A free app runs it on your laptop.
When the AI runs on your machine, your words never leave it. No training, no reviewers, no retention policy, no court order to a company holding your chats. LM Studio’s documentation puts it simply: “Nothing you enter into LM Studio when chatting with LLMs leaves your device.” Once you’ve downloaded a model, it works with the Wi-Fi off.
Open models have caught up fast. Stanford’s 2025 AI Index found the gap between the best closed and best open model on a popular head-to-head ranking shrank from 8% to 1.7% in about a year. Laptop-sized models are smaller than those, but for writing and summarizing they’re often plenty.
A few ways to try it:
- LM Studio: a friendly app for Mac, Windows and Linux. Free, though the app itself isn’t open source.
- Ollama: open source and popular with tinkerers. It now offers cloud models too, so check which kind you’re running.
- Jan: an open-source, ChatGPT-style app that can run fully offline, with optional cloud connections.
- GPT4All: an open-source local chatbot from Nomic.
- edgar: our app at JobKick, built for writing and editing documents. It can run its model entirely on your Mac. edgar Cloud is optional, and it tells you every time your text leaves your device.
Where local AI has its own risks
Local isn’t magic. It moves the risk from someone else’s server to your own computer.
- Fake download sites. In 2025, Kaspersky found a fake DeepSeek site that was the top Google ad for “deepseek r1.” It offered to install Ollama and LM Studio, with malware bundled in that could watch everything you do in your browser. Download only from the official site, and be suspicious of ads.
- Booby-trapped model files. Security firm JFrog found about 100 models on Hugging Face, the biggest site for sharing AI models, built to run hidden code on the computer that loads them. Stick to well-known models from the big publishers, and use an app that downloads them for you.
- Leaving the door open. Cisco’s security researchers found 1,139 Ollama servers wide open on the internet in 2025, usable by anyone who found them. That happens when people set a local AI up to be reachable from other machines. If you’re not sure what that means, leave the default settings alone.
- Old software. Local AI apps have had serious security bugs, fixed in updates. Keep the app updated.
- Your laptop becomes the vault. Anyone who gets into your computer can read your saved chats. Use a password and disk encryption.
- “Local” apps with cloud switches. Several local apps can also use cloud models. Know which mode you’re in.
- Smaller can mean wrong. A model on your laptop is usually smaller than the big cloud ones and can make more mistakes. Check anything medical, legal or financial with a real professional, whichever AI you used.
What I’d do
- Look before you paste. A pasted email thread or a dropped-in PDF carries everything in it: health details, account numbers, other people’s names, your address in the letterhead. Skim it first, or keep it local, or keep it out.
- Turn off training in every cloud chatbot you use. The steps for each one are above.
- Strip the specifics. “A 45-year-old with this test result” works as well as your full name and date of birth.
- Don’t click “share” on anything private. Copy the text you need instead.
- Try one local app this week. Download it from the official site, pick a well-known model, and use it for the stuff you’d rather nobody saw.
I’m curious where you draw the line. Is there anything you’d never paste into ChatGPT? Or something you typed and later wished you hadn’t? Tell me in the comments.
Sources
- King, J., Klyman, K., Capstick, E., Saade, T., Hsieh, V. (Stanford, 2025), User Privacy and Large Language Models; Stanford HAI, Be careful what you tell your AI chatbot. Six developers’ privacy policies.
- Google, Gemini Apps Privacy Hub, updated September 2026.
- Opt-out steps: OpenAI, Data controls in ChatGPT; Google, Manage your Gemini Apps activity; Anthropic, How do I change my model improvement privacy settings?; Microsoft, Microsoft Copilot privacy controls; X, About Grok; Engadget (Sept 2026), How to stop AI companies from training on your data.
- Anthropic (Aug 2025), Updates to our consumer terms.
- OpenAI (June 2025, updated Oct 2025), How we’re responding to The New York Times’ data demands; OpenAI (Nov 2025), Fighting the New York Times’ invasion of user privacy; ABA Journal (Jan 2026), ChatGPT creator must turn over 20M chat logs.
- TechCrunch (July 2025), Sam Altman warns there’s no legal confidentiality when using ChatGPT as a therapist.
- Fast Company (July 2025), Google is indexing ChatGPT conversations; Fortune (Aug 2025), OpenAI removes ChatGPT search feature; Forbes (Aug 2025), xAI published hundreds of thousands of Grok conversations.
- TechCrunch (June 2025), The Meta AI app is a privacy disaster; TechCrunch (Apr 2026), PSA: if you use the Meta AI app….
- OpenAI (Mar 2023), March 20 ChatGPT outage: here’s what happened.
- National Cybersecurity Alliance & CybSafe (Sept 2025), Oh, Behave! 2025–2026: 65% now use AI, but majority remain untrained on risks. More than 6,500 people in 7 countries.
- KFF (Mar 2026), Tracking poll on health information and trust: use of AI for health information and advice. 1,343 U.S. adults.
- Chatterji, A. et al. (NBER Working Paper 34255, Sept 2025), How People Use ChatGPT. About 1.1 million sampled conversations.
- Stanford HAI (2025), AI Index Report: Technical performance.
- LM Studio, Offline operation; Ollama; Jan; GPT4All.
- Kaspersky Securelist (June 2025), BrowserVenom mimics DeepSeek to use a malicious proxy.
- JFrog (Feb 2024), Data scientists targeted by malicious Hugging Face ML models with silent backdoor.
- Cisco (Sept 2025), Detecting exposed LLM servers: a Shodan case study on Ollama; Wiz (June 2024), Probllama: Ollama remote code execution vulnerability (CVE-2024-37032).
 JobKick support
Comments
Loading comments…